NIS2: How to Build Cyber Resilience in the Supply Chain
News Aug 12, 2025Updated: Dec 06, 2025
Practical implications of European regulations
Concrete contribution of supply chain security, incident response and training processes to institutions within the scope of NIS2 and ways of implementation.
“Translating compliance into operational resilience: supplier management and incident response play a key role.”
NIS2 and Cyber Resilience
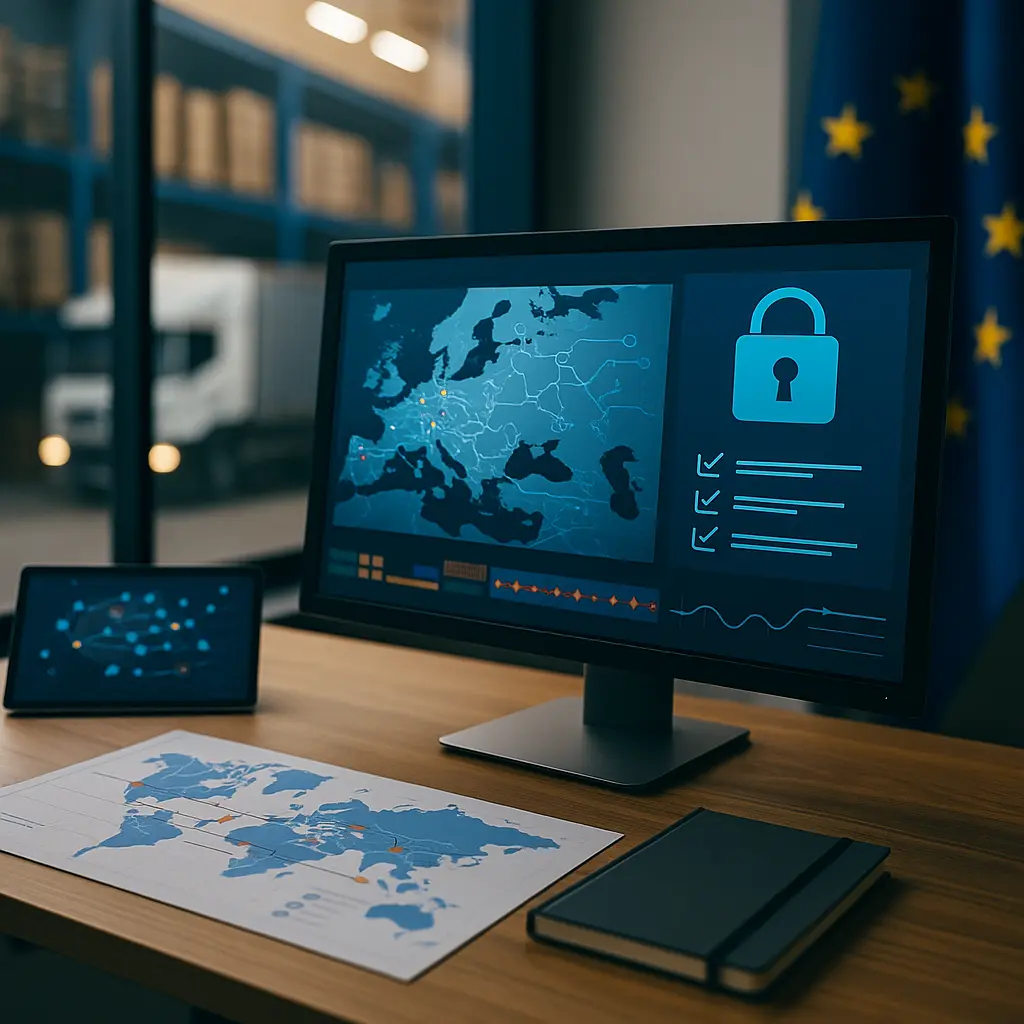
NIS2 covers the supply chain as well as critical service providers. Institutions; It needs standardized processes for risk-based security, incident notifications, and supplier management.
Recommended Approach
Supplier risk assessment matrices and minimum safety requirements
Incident response plan, communication and evidence retention processes
Continuing education, testing and drills
Conclusion: Regulatory compliance is an opportunity for true operational resilience.